Switzerland software delivery: the revised FADP, QR-bill, TWINT and the federal e-ID
A Switzerland-facing software project turns on five decisions before a proposal is comparable: which law and authority govern data protection now that the revised Federal Act on Data Protection applies, how personal data may be disclosed abroad, whether QR-bill or TWINT belongs at checkout, whether the federal e-ID affects sign-up, and when German, French or Italian interfaces are required.
Submit a project Explore custom engineeringReviewed by Huy Nguyen (David), CEO · Updated 24 Oct 2026 · 13 min read
OutsourcingVN is operated by Netbase JSC, and this guide is written by a supplier that would welcome your project. It separates what Swiss law actually requires from what Netbase can evidence about its own practice, with regulator and government sources named throughout for your own legal and tax advisers to verify. The guides index covers other markets, and the market index shows which question each one answers first.
Contents
- Who enforces data protection for a Switzerland-facing product?
- What can Netbase evidence for a Switzerland brief?
- Which requirement sits with which decision owner?
- Which steps come before a Switzerland-facing launch?
- Worked scenario: a Swiss shopper pays with TWINT
- What has Netbase built that is relevant to a Switzerland brief?
- Which questions should you ask a supplier?
- What usually goes wrong?
- How this guide is sourced and where it stops
- Common questions
- Plan the first release
Who enforces data protection for a Switzerland-facing product?
Switzerland is outside the European Union, so GDPR does not apply there directly. Since 1 September 2023 the revised Federal Act on Data Protection (FADP) has governed processing of personal data in Switzerland, replacing the Federal Act of 19 June 1992. The Federal Data Protection and Information Commissioner (FDPIC) is the federal authority that supervises compliance. Under Article 24, a controller must notify the FDPIC as quickly as possible of any data security breach that is likely to lead to a high risk to the data subject's personality or fundamental rights.
The FADP sets its own rule for sending personal data outside Switzerland, separate from the EU's own transfer regime. Article 16 lets a transfer go ahead without extra safeguards where the Federal Council has judged the destination adequate; the states, territories and international bodies it has judged adequate are listed in Annex 1 of the Data Protection Ordinance. Outside that list, a Switzerland-facing system needs its own safeguard: data protection clauses in the contract, notified to the FDPIC before the data is disclosed, which a data processing agreement can carry; standard data protection clauses the FDPIC has approved, issued or recognised beforehand; binding corporate rules approved in advance; or an agreement under international law such as Convention 108+. Article 17 keeps a narrow set of exceptions beyond those routes.
What can Netbase evidence for a Switzerland brief?
Procurement, security and data protection reviewers tend to ask for the same statements. These are the ones Netbase can give.
- Compliance practices. Netbase's compliance practices are GDPR alignment for data privacy in Europe, HIPAA-aligned methodologies for healthcare data handling, and CCPA compliance for clients with U.S. customer bases. Your advisers assess the Switzerland-facing processing against the revised FADP and the Article 16 disclosure rule above.
- Security practices. Security practices include secure code review and version control, role-based access control, MFA for admin dashboards, contributors under NDA, and NDAs and DPAs on request. A data processing agreement written for the Switzerland-facing system sits on top of this baseline.
- Markets and hours. Netbase clients are in the United States, Europe and Asia-Pacific, and most projects come from clients outside Vietnam. Netbase has worked with clients in 80 countries. The Hanoi office works Monday to Saturday, 9:00-18:15 Vietnam time (UTC+7), and support coverage follows those days. In Zurich that working day falls at 3:00-12:15 during the Swiss winter and 4:00-13:15 during the Swiss summer.
Which requirement sits with which decision owner?
A Swiss brief spans several owners inside the buying organisation, and a proposal that conflates them is the fastest way to miss one once the contract is signed.
| Decision area | What Swiss rules and practice expect | What a supplier can evidence | Who decides |
|---|---|---|---|
| Data protection | Processing consistent with the revised FADP, a breach report to the FDPIC without undue delay | A data processing agreement, an access matrix, a tested breach-response plan | Data protection officer |
| Disclosure abroad | A destination on the Federal Council's Annex 1 list, or a safeguard such as FDPIC-approved clauses | A documented transfer route and the safeguard that backs it | Data protection officer |
| Payments | QR-bill on invoices, TWINT alongside cards at checkout | Payment flows tested against the agreed rails, with a fallback for a failed transfer | Product owner with payments provider |
| Identity | The state-recognised federal e-ID, held in the swiyu wallet, where a product chooses to accept it | A tested integration where the product reaches the e-ID flow | Product owner |
| Accessibility | The Disability Equality Act and the federal eCH-0059 standard for federal digital services | Per-journey test results with assistive technology, a defect log | Product or service owner |
| Language | A language boundary the buyer's legal adviser confirms across German, French and Italian | A named copy owner per language and a tested translation workflow | Localisation owner |
Ask for this table filled in, not just a general compliance statement, before shortlisting a supplier.
Which steps come before a Switzerland-facing launch?
-
Confirm the FADP processing duties
Write down what personal data the product collects, stores or shares, who holds the data protection officer role, and how a breach is reported to the FDPIC.
-
Check disclosure abroad against the adequacy list
Decide where every personal-data field travels, and whether the destination is on the Federal Council's Annex 1 list or needs its own safeguard.
-
Add QR-bill and TWINT
Support the QR-bill format on invoices and offer TWINT alongside cards at checkout as a second payment rail.
-
Scope the e-ID and language interfaces
Decide whether any journey should accept the federal e-ID, and which screens and contracts need German, French or Italian.
-
Decide go-live readiness
Check the data map, the disclosure-abroad route and the payment and language scope against the plan, and record the decision with its owner.
-
Launch and keep the record current
Publish or update the accessibility statement, keep the QR-bill and TWINT integrations tested, and review all items again at the next major release.
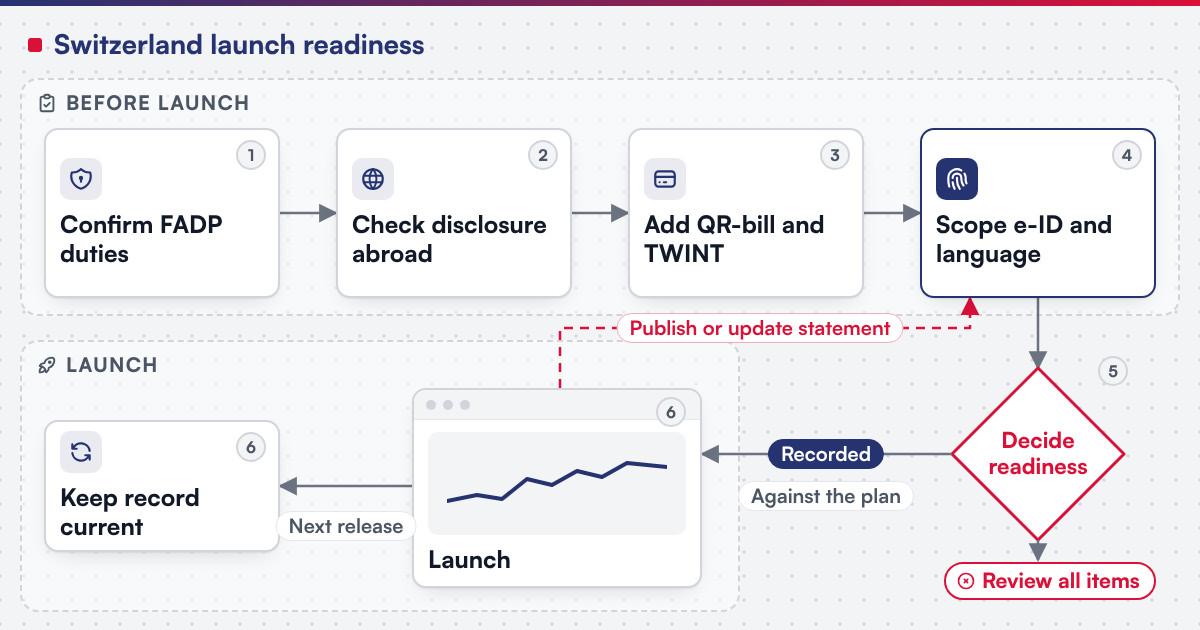 (opens the full-size diagram in a new tab)
Worked scenario: a Swiss shopper pays with TWINT
A subscription retailer launches a Swiss storefront where shoppers pay with TWINT alongside cards, and invoices carry a QR-bill.
-
TWINT selected
The shopper opens the TWINT app and scans the checkout's QR code or terminal code instead of entering card details
- Owner
- Engineering
-
Payment confirmed
The shopper confirms the payment inside the TWINT app
- Owner
- Shopper, in the TWINT app
-
Timeout handled
If the payment is not confirmed in time, the checkout falls back to a card retry rather than leaving the order stuck
- Owner
- Product owner
-
Invoice issued
A follow-up invoice, where one is needed, carries a QR-bill with the Swiss QR code encoding the payment details
- Owner
- Finance systems
-
Receipt issued
The confirmation and receipt are sent in the shopper's chosen language, with the amount, order number and support contact
- Owner
- Localisation owner
-
Support view
An agent can see the payment status for a ticket, not the underlying banking details
- Owner
- Support lead
A proposal that cannot describe step 3, specifically what the checkout does when a TWINT payment does not confirm in time, has not yet scoped Swiss payments for this product.
What has Netbase built that is relevant to a Switzerland brief?
Netbase has delivered product personalisation on client print stores, including online designers and configurators for catalogue covers and custom bags, for print-commerce clients in Singapore, Switzerland, Hong Kong, Germany, China, the United Kingdom, the Netherlands, the United States, Poland, France and Portugal. The published record closest to this guide includes order-flow customisations for a German invitation-card printer, covering hidden design buttons on the cart page, a quantity dropdown, and the product key and ordered quantity written into the print PDF file name. The online designer feature builds record covers that engagement and five other print businesses, and the product personalisation and online design solution scopes configurator work of this kind.
Which questions should you ask a supplier?
- Who signs the data processing agreement, and who is named controller? Expect a clear answer before contract, not during a breach.
- Which safeguard backs each cross-border data flow? Ask for the Annex 1 list entry or the approved clause, not just a claim that a safeguard exists.
- How does checkout handle TWINT alongside cards, and what happens when a payment does not confirm in time? A vague answer usually means the path has not been tested.
- Does our product need to accept the federal e-ID, and who holds that integration? This usually stays with the buyer, with the supplier building inside the access granted.
- Who owns German, French and Italian copy, and how does a change reach production? Translation drift across three languages is easiest to catch before launch, not after.
- How do you test against the federal accessibility standard? Ask for real assistive-technology testing, not a tool report alone.
What usually goes wrong?
- A Swiss brief is scoped as if GDPR applied directly. Signal: no one has named the FADP, the FDPIC or the Annex 1 adequacy list. Owner: the data protection officer.
- Disclosure abroad is decided after the hosting provider is already chosen. Signal: a cross-border flow with no documented safeguard. Owner: the data protection officer, scoping this at discovery.
- A checkout is built around cards first, with TWINT bolted on at the end. Signal: the payment flow needs a disruptive rework rather than an addition. Owner: the product owner, who should put both rails in the same discovery estimate.
- One language is translated and the other two assumed to follow. Signal: French or Italian screens and generated documents drift out of date after the first release. Owner: the localisation owner.
How this guide is sourced and where it stops
This guide draws on the revised Federal Act on Data Protection's own English text, the Federal Data Protection and Information Commissioner's own pages on cross-border transfer and the adequacy list, SIX Group's own description of the QR-bill standard, TWINT's own description of its payment service, the federal administration's own accessibility page, and the federal e-ID's own page on the 2025 referendum result and the e-ID itself, all checked on 2026-10-24, together with company statements and delivery evidence approved in the OutsourcingVN claim register. It is written for product, procurement and operations leads scoping a Switzerland-facing brief; it does not decide which safeguard or language scope fits your organisation.
Plan the next step for your project
Common questions
No. Switzerland is outside the European Union, and GDPR does not apply there directly; the revised Federal Act on Data Protection, supervised by the FDPIC, is the law a Switzerland-facing product follows. GDPR only becomes relevant where a product separately processes the data of people in the EU.
The two are separate decisions. Switzerland's own Federal Council keeps its own Annex 1 list of countries it judges adequate for data leaving Switzerland; the EU decides separately, and the FDPIC records an EU decision of 2000 confirmed on 15 January 2024.
Often both, because each covers a different payment moment: the QR-bill carries the payment details of an invoice, and TWINT is a checkout option alongside cards.
Not necessarily. Swiss voters approved the federal e-ID law in a referendum on 28 September 2025, and the state-recognised e-ID will let Switzerland's residents prove their identity electronically, issued by the federal government and held in the swiyu wallet; many products can launch without it and add acceptance once the e-ID and the integration are ready.
Not always. Many buyers ship the journeys used most in the languages their customers actually need and keep less-used screens in one language, provided the boundary is written down, your legal adviser confirms which texts must appear in German, French or Italian, and a named owner reviews each language before release.
Yes, when the invoice format, the payment flow and the fallback behaviour are scoped with the same care as any other method, and tested against the published implementation guidelines before launch.
Plan the first release
Bring your FADP role split, your disclosure-abroad safeguard, your QR-bill and TWINT scope, and your German, French and Italian language boundary. The data security and compliance guide lists the contract questions behind the data protection row, and the time zone and collaboration guide covers how overlap and handoff are agreed for a European working day. The Germany guide covers works-council consultation and German e-invoicing formats for a neighbouring German-speaking market, the France guide covers CNIL guidance and the French e-invoicing reform, and the Netherlands guide covers Peppol e-invoicing and the Dutch supervisory authority, for buyers weighing other European markets alongside Switzerland.
Custom Product Engineering is the service for a bounded build, and global delivery explains how remote delivery is organised. OutsourcingVN is Netbase's own outsourcing-services platform: submit a project with your Switzerland-facing scope, and a person will reply with whether discovery or a bounded implementation is the right next step.
Work behind this guide
Netbase built custom features into the online designers and order flows of six unnamed print businesses: a photo background remover with more than 30 cartoon filter styles, a page-thumbnail preview bar, invitation-card order rules, finished-size rulers, wallpaper sample ordering and a label website with four design paths. No result is claimed.
Keep ReadingRelated services and solutions
 Custom product engineering for a bounded release outcome
One defined release of your product, built to named outcomes and handed over with acceptance evidence.
Learn More
Sources
- Federal Act on Data Protection (FADP), English translation, status 1 September 2023
- Federal Data Protection and Information Commissioner (FDPIC), Cross-border transfer of personal data
- Federal Data Protection and Information Commissioner (FDPIC), Adequacy
- SIX Group, QR-bill
- TWINT
- Federal Office of Information Technology, Systems and Telecommunication, Accessibility in the federal administration
- Swiss e-ID, e-ID law approved at the ballot box