Sweden software delivery: GDPR enforcement, accessibility, Peppol, BankID and Swish
A Sweden-facing release usually turns on five decisions that sit outside the feature list: who enforces data protection and how a breach is reported, which accessibility standard the product commits to, whether the buyer needs e-invoices on the Peppol network, whether BankID and Swish belong at sign-in and checkout, and which language ships first. Settle those before comparing proposals.
Submit a project Explore custom engineeringReviewed by David Nguyen (CEO) · Updated 13 Oct 2026 · 12 min read
OutsourcingVN is operated by Netbase JSC, so this guide is written by a supplier that would like your project. It sets out what Netbase can evidence for a Swedish brief, points to the official references your own advisers should read in full, and names the decisions that stay with you. The guides index lists guides for other markets, and the market index compares the first question each one raises.
Contents
- Who enforces data protection for a Swedish-facing product?
- What can Netbase evidence for a Swedish brief?
- Which requirement sits with which decision owner?
- Which steps come before a Swedish-facing launch?
- Worked scenario: a Swedish shopper signs in and pays
- What has Netbase built that is relevant to a Swedish brief?
- Which questions should you ask a supplier?
- What usually goes wrong?
- How this guide is sourced and where it stops
- Common questions
- Plan the first release
Who enforces data protection for a Swedish-facing product?
GDPR applies across the European Union, and Sweden reaches it through its own national supervisory authority, the Swedish Authority for Privacy Protection (IMY), rather than a separate Swedish law layered on top. A controller must have a lawful basis for each use of personal data, honour access, correction, erasure and portability requests, and tell its supervisory authority of a qualifying breach within 72 hours of becoming aware of it. Fines can reach the higher of €20 million or 4% of global annual turnover. IMY publishes guidance, takes complaints from individuals and can open supervisory reviews and impose corrective measures.
None of that changes because the development team sits outside Sweden. What changes is who signs the processing agreement, who is named as controller or processor, and who answers IMY's questions if a Swedish user complains. A buyer should decide those three roles before discovery starts, not after a defect is found.
What can Netbase evidence for a Swedish brief?
Procurement, security and data protection reviewers tend to ask for the same four statements. These are the ones Netbase can give.
- Compliance practices. Netbase's compliance practices are GDPR alignment for data privacy in Europe, HIPAA-aligned methodologies for healthcare data handling, and CCPA compliance for clients with U.S. customer bases. Deciding how GDPR applies to your own product and who your Swedish data protection officer is remains your organisation's task.
- Security practices. Security practices include secure code review and version control, role-based access control, MFA for admin dashboards, contributors under NDA, and NDAs and DPAs on request. A data processing agreement for a Swedish-facing system sits on top of this baseline.
- Information security management. Netbase JSC holds ISO 27001 certification for information security management. This is a company-level certification describing Netbase's own management system; it is never a guarantee extended to a specific product or hosting arrangement built for a client.
- Markets and language. Netbase clients are in the United States, Europe and Asia-Pacific, and most projects come from clients outside Vietnam. Delivery communication is in English, so a Swedish-facing product's own localisation into Swedish is scoped as a project task, with a named Swedish copy owner.
Which requirement sits with which decision owner?
A Swedish brief usually spans five separate owners inside the buying organisation. Splitting the requirement from the evidence from the decision keeps a proposal from promising more than one team can check.
| Decision area | What Swedish and EU rules expect | What a supplier can evidence | Who decides |
|---|---|---|---|
| Data protection | A lawful basis per use, a 72-hour breach report to IMY, honoured subject rights | A data processing agreement, an access matrix, a tested breach-response plan | Data protection lead |
| Accessibility | DIGG's guidelines point public-sector websites and apps to the EN 301 549 standard, based on WCAG; private-sector practice increasingly follows the same bar | Per-journey test results with assistive technology, a defect log | Product or service owner |
| E-invoicing | Suppliers to covered public-sector buyers send a structured EN 16931 e-invoice over Peppol | A Peppol access-point connection and a tested invoice export | Finance systems owner |
| Payments and identity | Swedish users commonly expect BankID for sign-in on actions that need verified identity, and Swish alongside cards at checkout | A tested BankID flow with a designed fallback, and Swish integrated alongside card payments | Product owner with payments provider |
| Language | Swedish copy for consumer journeys; English is common for B2B tools | A named Swedish copy owner and a tested translation workflow | Localisation owner |
Ask for this table filled in, not just a general compliance statement, before shortlisting a supplier.
Which steps come before a Swedish-facing launch?
-
Map the data flows per use
Record what personal data the product collects, stores or shares for each use, and which GDPR lawful basis applies to it.
-
Name the accessibility standard
Decide what a public-sector-facing service must meet under DIGG's guidelines, and what a private product will commit to for its own users.
-
Connect to Peppol for e-invoicing
If the product bills a Swedish public body, join the Peppol network so invoices reach the buyer in the EN 16931 format.
-
Add BankID and Swish
Decide which actions need BankID-verified identity, and offer Swish alongside cards, since many Swedish shoppers expect to pay from their banking app.
-
Decide go-live readiness
Check the data map, the accessibility test results, the Peppol connection and the identity, payment and language scope against the plan, and record the decision with its owner.
-
Launch and keep the record current
Publish or update the accessibility statement, keep the breach-response plan rehearsed, and review the five items again at the next major release.
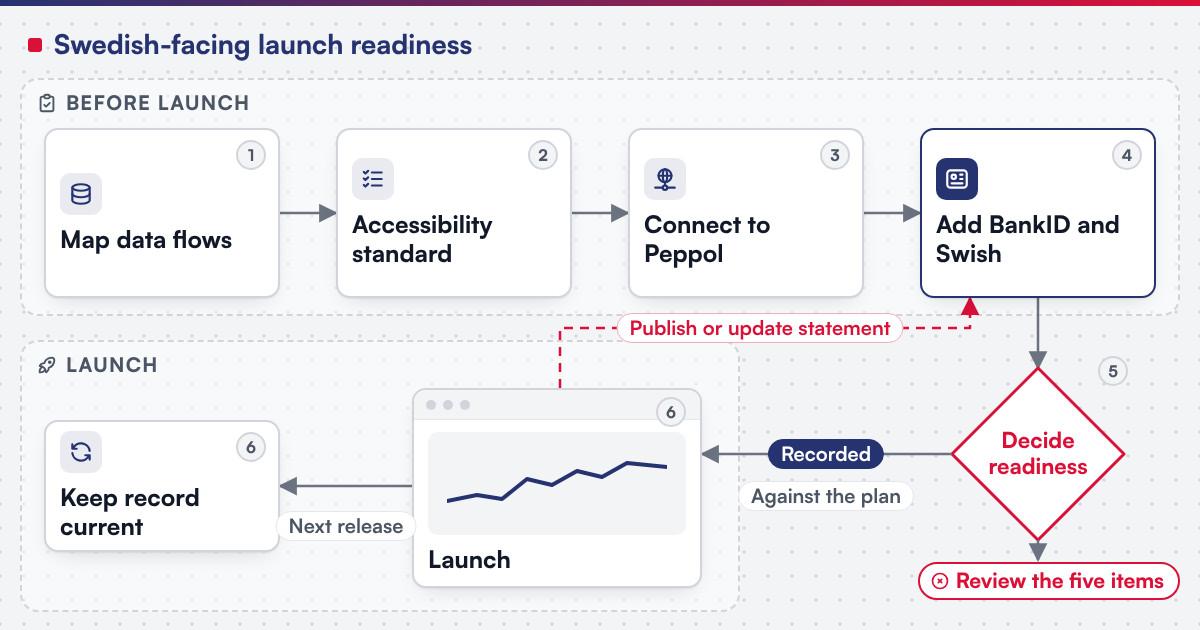 (opens the full-size diagram in a new tab)
Worked scenario: a Swedish shopper signs in and pays
A subscription retailer launches a Swedish storefront where returning shoppers sign in with BankID and pay with Swish alongside cards.
-
BankID sign-in
The shopper taps "Sign in with BankID"; the app confirms with a PIN or biometric, and the callback records a verification status, not raw identity data
- Owner
- Engineering
-
Account matched
A returning shopper's verified identity is matched to the existing account by a tested rule, so no duplicate account is created
- Owner
- Engineering with support
-
Checkout offers Swish
The shopper picks Swish alongside cards; the request goes to their banking app for approval
- Owner
- Engineering
-
Timeout handled
If the Swish approval does not arrive in time, the checkout falls back to a card retry rather than leaving the order stuck
- Owner
- Product owner
-
Receipt issued
The confirmation and receipt are sent in Swedish, with the amount, order number and support contact
- Owner
- Localisation owner
-
Support view
An agent can see the sign-in and payment status for a ticket, not the underlying BankID or bank account details
- Owner
- Support lead
A proposal that cannot describe step 4, specifically what the checkout does when Swish does not confirm in time, has not yet scoped Swedish payments for this product.
What has Netbase built that is relevant to a Swedish brief?
The closest published evidence for a Swedish brief is European commerce and product work. For Rebelo AG, a Portuguese printer, Netbase set up a 3D preview in the online designer for boxes and other multi-sided products, live in about three and a half months; the Rebelo AG 3D product preview record has the detail, and it is European work, not Swedish. Netbase has also built web-to-print stores with the same kind of online design tool for print businesses in Singapore, France, the Netherlands and South Korea; the four-country web-to-print record covers the design-tool scope. Separately, Netbase JSC's Clutch profile carries client reviews from businesses in Romania, Spain, Sweden, France, Denmark, the Netherlands and Belgium, published between October 2020 and June 2021. One of them is from Sweden: Olof Christensson, CEO, Skelderwikens Brygghus AB (Sweden), reviewing "Web Dev for Consumer Goods Company" on Clutch, 2020-10-24, rated 5.0, wrote: "Their Quick response in every step was impressive." Netbase is also reviewed on other platforms; Sam Coldwell, in a Trustpilot review from the United Kingdom published 2024-07-26 and rated 5 stars, wrote: "We've been using the NB designer over the last few years and had nothing but rave reviews from customers who use it. We've also received excellent and timely support from the team at Netbase."
Which questions should you ask a supplier?
- Who signs the data processing agreement, and who is named controller? Expect a clear answer before contract, not during a breach.
- What exactly does your security and compliance statement cover? A precise answer says what it does not cover as well as what it does.
- How do you test against DIGG's accessibility guidelines? Ask for real assistive-technology testing, not a tool report alone.
- Can you show a Peppol invoice export from a past project? Ask for the structure, not just a claim that it exists.
- Who holds the BankID and Swish merchant relationships? These usually stay with the buyer, with the supplier building inside access you grant.
- Who owns the Swedish copy, and how does a change reach production? Translation drift is easiest to catch before launch, not after.
What usually goes wrong?
- Compliance copied from a company page straight into a proposal. Signal: no one has actually tested this specific product's data flows, access rules or breach-response plan. Owner: the data protection lead, who should ask for product-specific evidence rather than a restated policy.
- Accessibility testing left until the week before release. Signal: a backlog of defects surfaces only once the launch date is already fixed and hard to move. Owner: the product owner, who should schedule assistive-technology testing alongside each sprint, not at the end.
- BankID or Swish added after checkout and sign-in are already built around other methods. Signal: a late, disruptive change to the identity or payment flow. Owner: the product owner, scoping both at discovery.
- Swedish copy translated once and never re-tested. Signal: error messages and generated documents drift out of Swedish after the first release. Owner: the localisation owner.
How this guide is sourced and where it stops
This guide draws on IMY's own description of its role, DIGG's guidance on digital accessibility standards, the European Commission's eInvoicing country sheet for Sweden, the Swedish Parliament's published text of the 2018 e-invoicing law, the European Commission's Your Europe business page on GDPR, and Swish's own site, all checked on 2026-10-13, together with company statements and delivery and review evidence approved in the OutsourcingVN claim register. It is written for product, procurement and operations leads scoping a Swedish-facing brief. It does not decide which accessibility standard or data protection role fits your organisation; your own advisers make that call.
Plan the next step for your project
Common questions
The regulation itself is the same across the European Union; what differs by country is which national authority enforces it, and in Sweden that authority is IMY. Check IMY's current guidance rather than assuming every member state applies it identically.
No. The mandate covers invoices to covered public-sector buyers, which travel over the Peppol network in the structured EN 16931 format. Business-to-business e-invoicing is a separate commercial decision.
Not always. Many buyers ship the journeys Swedish customers use most in Swedish and keep less-used screens in English, provided the boundary is written down and a named owner reviews Swedish copy before each release.
Yes, when the identity flow, the checkout and the fallback behaviour are scoped with the same care as any other method, and tested against real accounts before launch.
The business owner, by naming which actions need verified identity; a product can launch with a simpler sign-in and add BankID later if that boundary is agreed in writing.
Plan the first release
Bring your data protection role split, your accessibility standard, your Peppol decision, and your BankID, Swish and Swedish-language scope. The data security and compliance guide lists the contract questions behind the data protection row, and the time zone and collaboration guide covers how overlap and handoff are agreed for a European working day. For neighbouring markets, the Netherlands guide covers Peppol and Dutch payment habits under the same EU law base, and the Germany guide covers works-council consultation and German e-invoicing formats; if you are also weighing a European-based delivery location, Vietnam vs Poland for software outsourcing compares that decision directly.
Custom Product Engineering is the service for a bounded build, and global delivery explains how remote delivery is organised. OutsourcingVN is Netbase's own outsourcing-services platform: submit a project with your Swedish-facing scope, and a person will reply with whether discovery or a bounded implementation is the right next step.
Work behind this guide
Go-live took about three and a half months.
Keep Reading
The stores run on WooCommerce and WordPress, with a design tool in Angular JS or Vue.js and PDF generation for production files.
Keep ReadingRelated services and solutions
 Custom product engineering for a bounded release outcome
One defined release of your product, built to named outcomes and handed over with acceptance evidence.
Learn More